Wallet Infrastructure
Deployment model, key management and policy, and compliance — everything wallet operations need, in one place. The configuration is assembled to fit your business and its regulation.
01
Three Choices
Where It Runs
Who Holds the Keys
How Keys Are Protected
02
Where It Runs
SaaS
On-premises
Runs in
ABC-hosted
Your infrastructure
Operated by
ABC
You
Build cost
Subscription fee
Yours
Keys and audit log
Instance separated per customer
Your internal network
Fits when
You want to start quickly
Network separation, users at scale
SaaS
- Runs in
- ABC-hosted
- Operated by
- ABC
- Build cost
- Subscription fee
- Keys and audit log
- Instance separated per customer
- Fits when
- You want to start quickly
On-premises
- Runs in
- Your infrastructure
- Operated by
- You
- Build cost
- Yours
- Keys and audit log
- Your internal network
- Fits when
- Network separation, users at scale
03
Who Holds the Keys
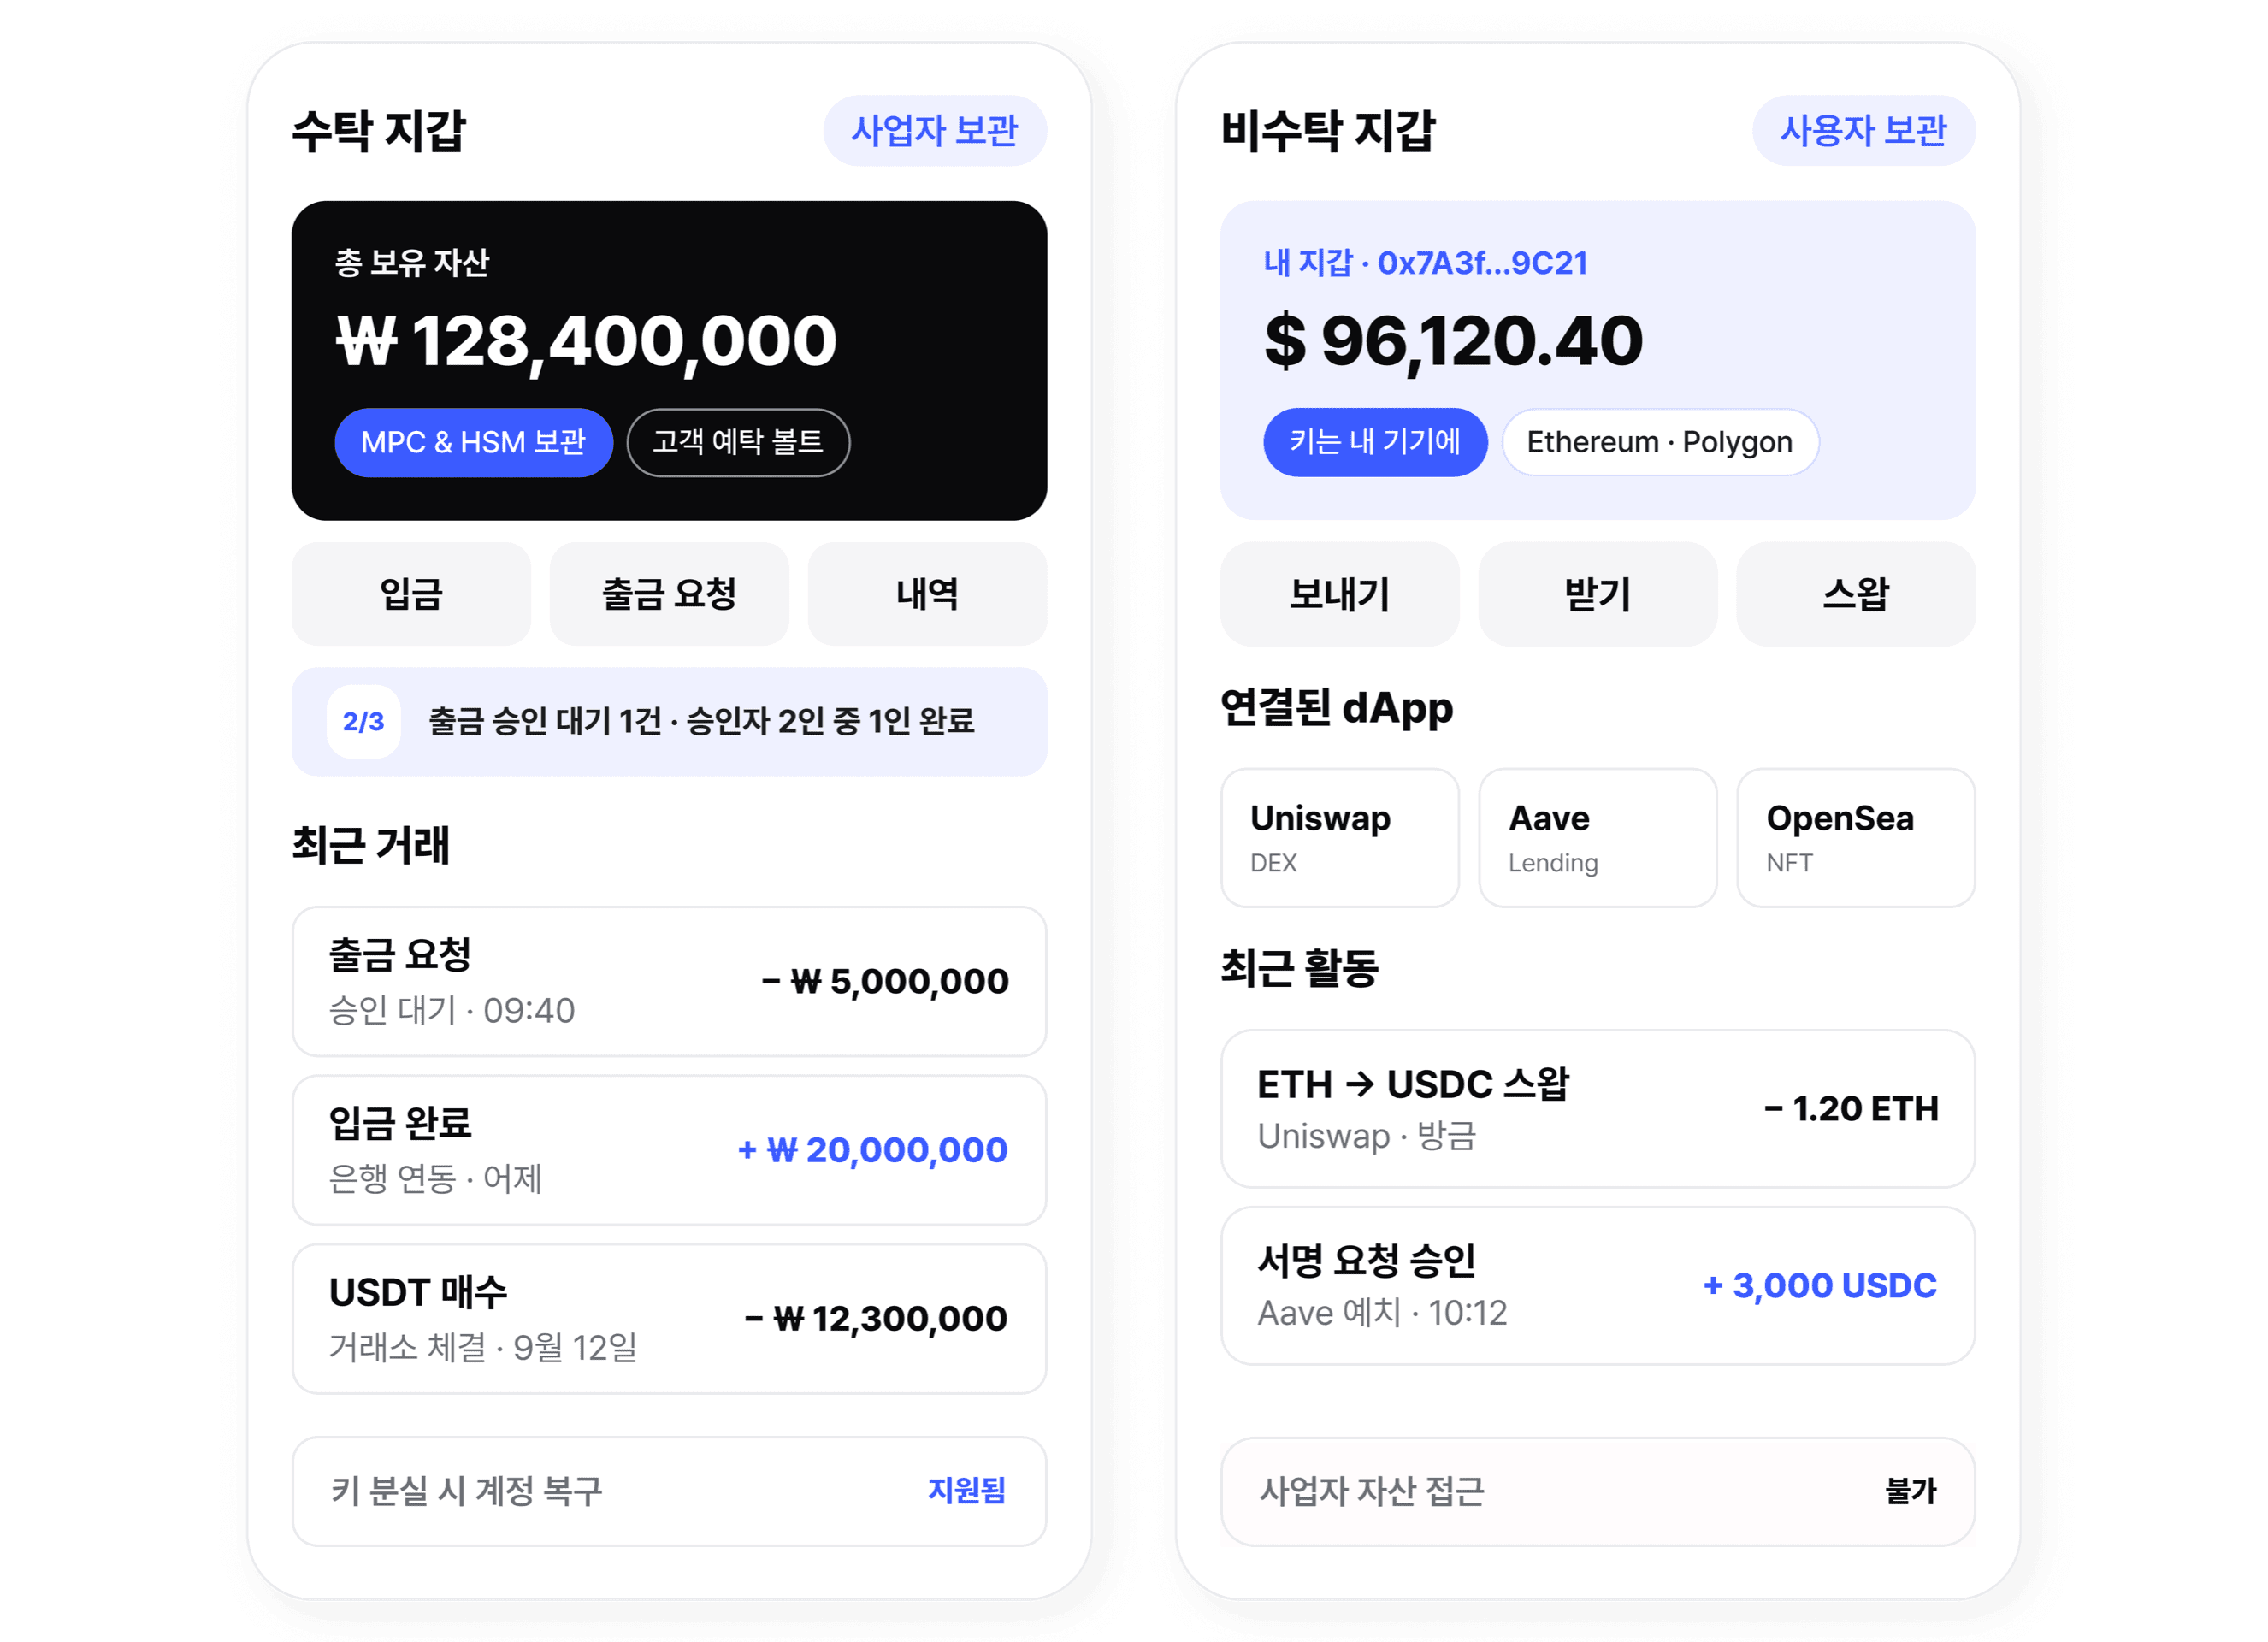
THE INSTITUTION HOLDS
Custodial
The institution holds assets and executes withdrawals on request.
- Requires a VASP licence — and obtaining one requires the custody service to be built first.
- AML and KYT obligations sit with the custodian of record.
- The user never handles a key, so losing one is not a product risk.
THE USER CONTROLS
Non-custodial
You provide the wallet without holding assets.
- No signature without the user's authentication, and the operator cannot move assets alone.
- Lose a device and a new sign-in restores the share.
- Because the user controls the assets directly, the institution is not the party bearing the regulatory obligation.
04
How Keys Are Protected
MPC
Multi-Party Computation- No single private key exists in complete form anywhere.
- Split into three shares held in separate environments.
- A 2-of-3 threshold — shares never reassemble, not even while signing.
HSM
Hardware Security Module- Keys are generated and held only inside the HSM.
- Signing completes inside the HSM, so the key is never exposed outside it.
- The devices meet international security certification standards.
MPC & HSM
Hybrid- A combination of the MPC and HSM approaches.
- Key shares are stored inside HSMs.
05
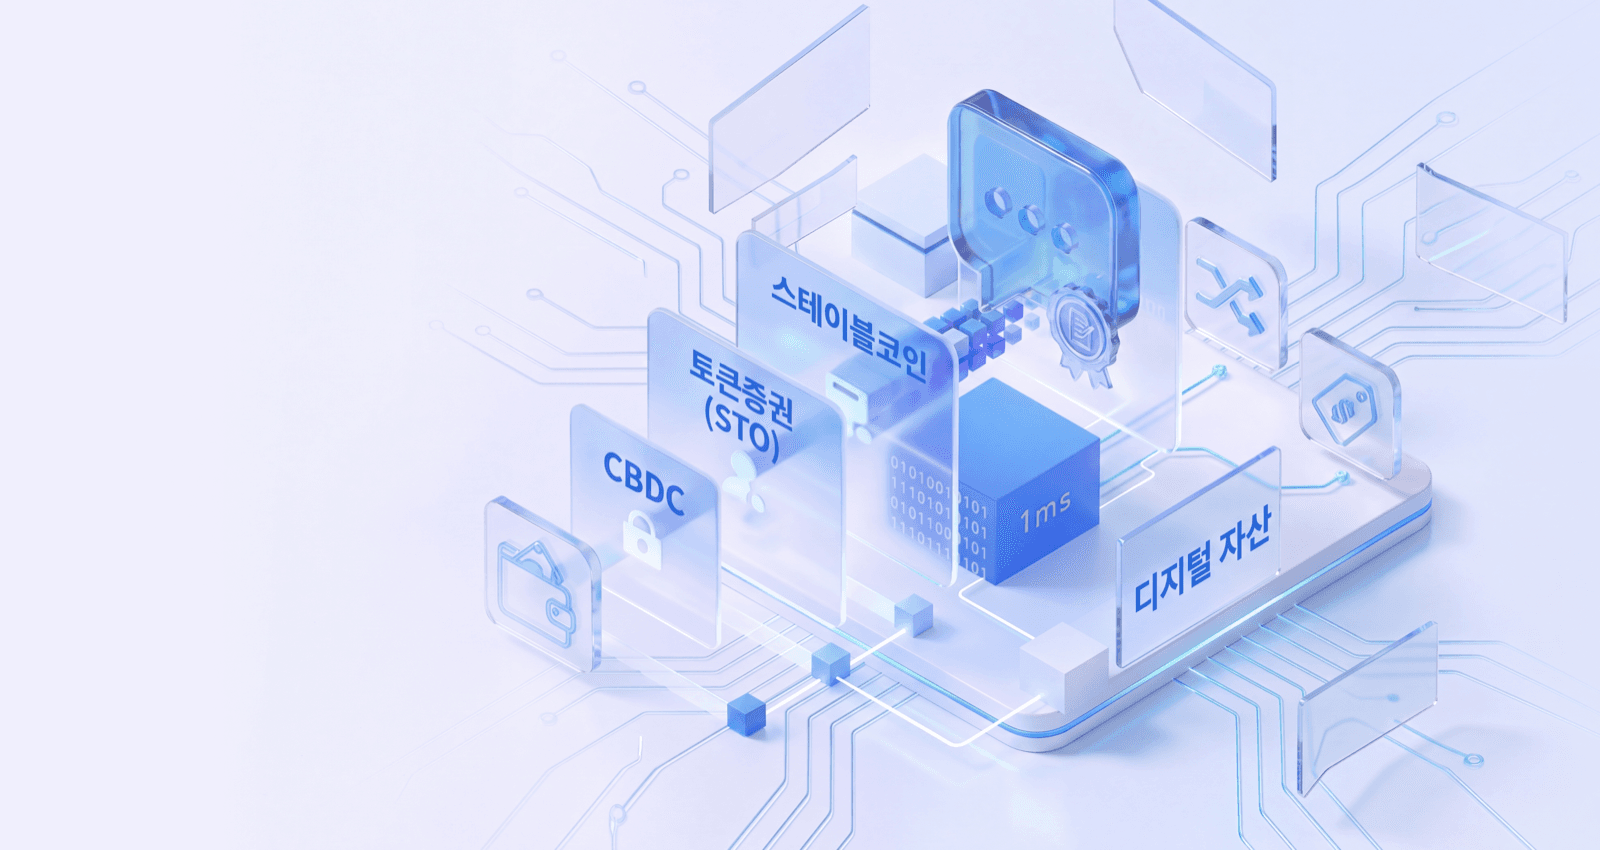
Wallet Orchestration
Manage multiple networks and asset classes as one, with fund flows and transactions orchestrated automatically.
06
Policy and Compliance
- Policy engine
- Designed to fit your internal policy
- Role-based permissions
- Requester, approver, and operations owner separated, with least privilege
- Audit trail
- Who requested, who approved, and which policy applied — all recorded
- KYT and Travel Rule
- Screens transactions and meets the obligation to exchange originator and beneficiary data
- AML and STR
- From detection through to reporting
Digital Asset Infrastructure That Fits Your Business, Start with ABC
Tell us your requirements and deployment constraints, and we'll propose a fit.